Cybersecurity: Portugal’s CNCS opens a discussion on certification
Businesses have an opportunity to discuss how organisational security is demonstrated. The starting point is the proposal, rather than assumptions about final rules.
Portugal’s National Cybersecurity Centre opened consultation on the preliminary QNRCS 2026 certification scheme on 20 November. Comments are invited until 4 December. The official page provides the proposal, the RJC profile and a mapping to ISO/IEC 27001. This is a consultation on draft documents, rather than the publication of final requirements.
The discussion concerns evidence as much as technology
The consultation raises a management question: the distance between saying that security exists and demonstrating how it works. An organisation may have a capable supplier, current tools and an attentive team. Yet if explaining its procedures depends on one person, the continuity of that work becomes difficult to assess. This is an editorial reading of the initiative, not a conclusion about requirements that may eventually be approved.
The quality of the questions matters. Which part of the operation is being examined? Which systems and suppliers fall within that examination? Who retains the evidence, and how long does it remain representative of the process? Asking these questions before selecting a solution can prevent an organisational exercise from becoming a premature technology purchase.
The hidden cost of poorly organised evidence
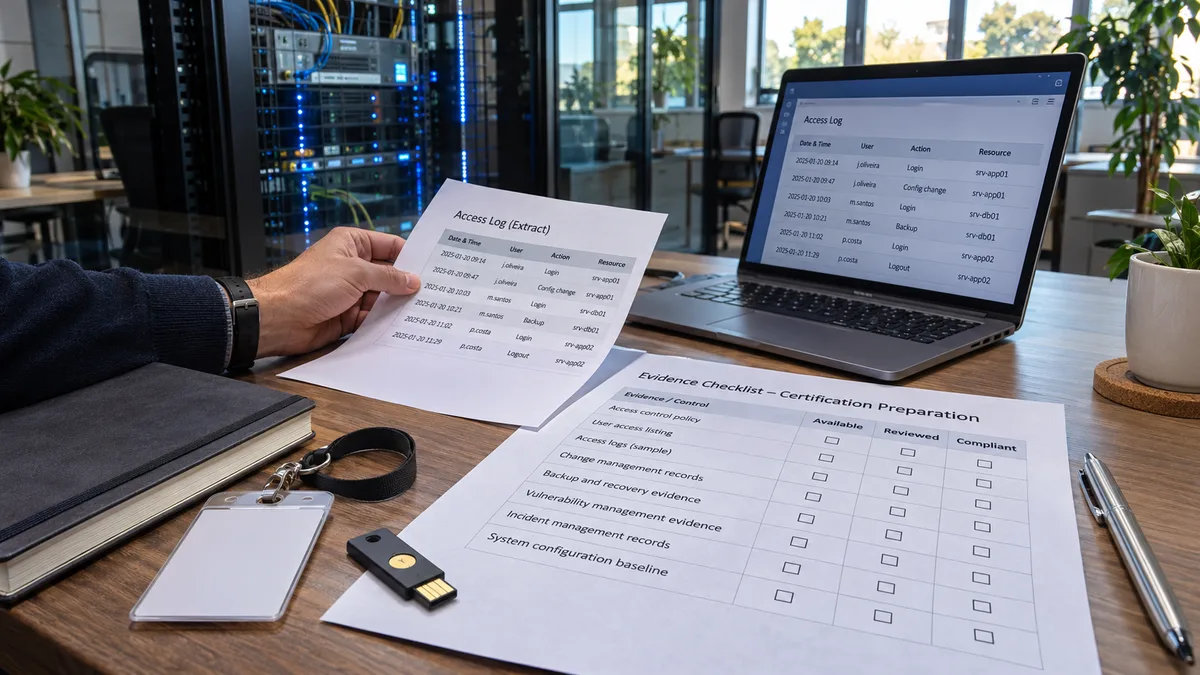
Consider a small company reviewing access permissions. Its accounting team knows about some accounts, its supplier manages others, and former employees still appear in a spreadsheet. This is a fictional scenario. It illustrates why gathering information can require more work than writing another document. A carefully prepared list does not, on its own, reconcile the procedure on paper with what actually happens.
A proportionate approach could begin with one defined process: people joining and leaving the organisation, for example. The team would identify the accounts involved, compare its procedure with a recent case and record the gaps it found. There would be no reason to describe this exercise as certification. Its result would be a clearer basis for deciding what to correct and which questions to raise during the consultation.
There is also a balance between detail and usefulness. A vague record demonstrates little; an excessive record may consume resources and collect information that was never needed. A consultation contribution becomes stronger when it explains that tension through a concrete example and proposes a workable alternative.
Read the scope before drawing conclusions
A reference to standards or a mapping table may help readers navigate related documents. It does not replace examining the scope, version and conditions of each instrument. Turning the existence of a mapping into a promise of automatic equivalence, or a universal obligation for every business, would be premature.
The starting point remains the official consultation page. A company wishing to participate should work from the published documents and distinguish its suggestions from the proposed wording. Useful public discussion depends on that precision: concrete experience, explained consequences and an opportunity to revise a solution before treating it as final.
The question behind the proposal
For me, this raises a question many businesses postpone: how do we demonstrate that security is part of everyday work? Buying a tool is an individual decision. Knowing who approves access, who oversees suppliers and who checks that a backup can be restored requires continuity.
Reading the proposal can help organise that conversation. Start by identifying the relevant documents and assigning their assessment to someone who understands the organisation’s systems and responsibilities. The name of a certification scheme alone does not establish that every business falls within its scope in the same way.
Contribute a concrete problem
A useful contribution describes a difficulty that can be examined. It might explain why a particular piece of evidence is difficult for a small team to produce, suggest an alternative and show how that alternative preserves the security objective. This is an example of preparing feedback, rather than a requirement taken from the proposal.
I would use a short record: document, provision, observed problem, practical consequence and suggested change. A specific argument is easier to assess than a broad statement of support or opposition.
What a business can do now
Even without deciding on certification, choose one process and look for its evidence. When the last employee left, was access revoked? Who can explain the procedure? Where was the action recorded?
My business reading of this consultation is that preparation begins by making existing practice visible and identifying what still relies on someone’s memory. Any decision about scope or requirements should rest on the applicable documents, the final version and an assessment of the organisation itself.
Sources consulted
- CNCS — consulta pública QNRCS 2026Centro Nacional de Cibersegurança. Date stated by the source: . Accessed: .